Question

Individual CUD Actions for an Entity

  • Oct 15, 2026 10:30 AM UTC
  • 15 replies
  • 98 views

Rajith
Sidekick (Partner)
Forum|alt.badge.img+6

Hi All,

Is it still not possible to individually grant/revoke CUD actions for an entity?

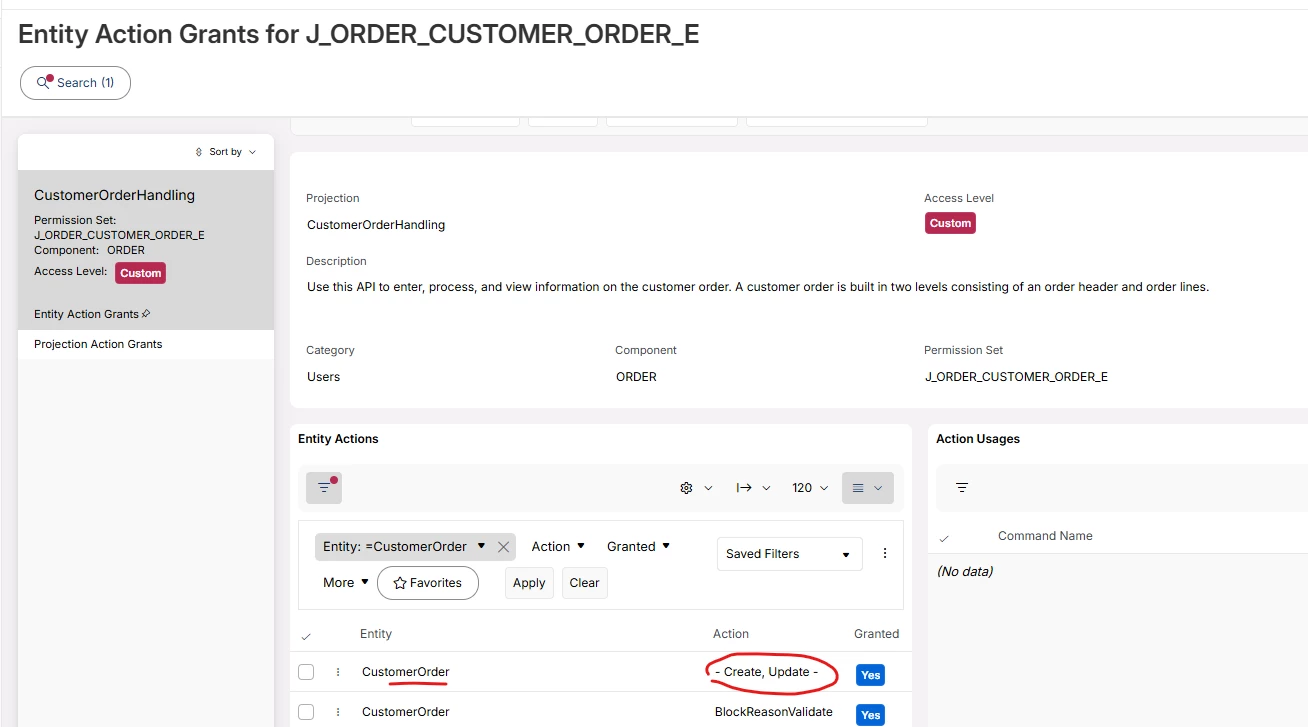
Say, when we grant CustomerOrderHandling, Role A wants to Create Customer Orders and Role B wants update Customer Orders but not create.

Looks like Actions - Create, Update - are bundled together so not possible.


Any workarounds please?

Events?

Modification?

Page Designer?


TIA.
15 replies

Rajith
Sidekick (Partner)
Forum|alt.badge.img+6
  • Author
  • Sidekick (Partner)
  • Oct 15, 2026 10:39 AM UTC


PhillBronson
Hero (Customer)
Forum|alt.badge.img+13
  • Hero (Customer)
  • Oct 23, 2026 4:18 PM UTC

​@Rajith what version of IFS are you on?


Rajith
Sidekick (Partner)
Forum|alt.badge.img+6
  • Author
  • Sidekick (Partner)
  • Oct 25, 2026 10:24 PM UTC

Hey ​@PhillBronson 

Application service update: 26.1.4

/tia Rajith


Forum|alt.badge.img+12
  • Hero (Customer)
  • Nov 11, 2026 1:53 AM UTC

This is not possible, at least not through the base Framework for projections handling in permission sets.

What you want to do is of course doable but would require customizations to add specific row level security handling. There are multiple ways of doing that, such Overriding and adding checks to Check_Insert__ and Check_Update__ in PLSQL Packages which checks whether the logged in user (fnd_session_api.get_fnd_user) meets your desired criteria (such as belonging to a specific user group for instance, or having a specific System privilege).

Note that modifying the PLSQL packages would NOT remove the +/edit buttons from the client files, but would result in errors if the user tried to do something your custom business logic says they should not be able to do.

You CAN customize customize the client to make the buttons disappear on conditions but it is a bit more complex as it requires enabling the CRUD actions based on the value of a global variable for instance.

I have done that in my organization where there was a requirement for users to be able to edit Purchase Orders but not be able to create them directly.


Rajith
Sidekick (Partner)
Forum|alt.badge.img+6
  • Author
  • Sidekick (Partner)
  • Nov 11, 2026 7:01 PM UTC

Cheers Simon, so modification is the only way so far.

Kind Regards


Abdul
Superhero (Partner)
Forum|alt.badge.img+20
  • Superhero (Partner)
  • Nov 11, 2026 9:43 PM UTC

Hi ​@Rajith,

Row level security could be achieved using ACL configuration, although, ACL could be only enabled for a user/user group and not for a functional/end user role.

I believe ACL is worth enough to give a try before going for customisation.


Rajith
Sidekick (Partner)
Forum|alt.badge.img+6
  • Author
  • Sidekick (Partner)
  • Nov 12, 2026 6:17 AM UTC

Hi Abdul,

I tried with ACL, but it doesn't seem to work. I have below ACL applied to PartHandling.


Filter:

(PART_NO IN ( 'RDP1' , 'RDP2' )) AND (fnd_session_api.Get_Fnd_User IN ( 'ITCONSULTANT1' ))


My requirement is above parts can be edited by ITCONSULTANT1 only and the rest can be edited by any user.


Best regards


Forum|alt.badge.img+12
  • Hero (Customer)
  • Nov 12, 2026 1:33 PM UTC

I could be wrong there but don’t ACLs only apply to the select statement, meaning the ability to RETRIEVE and display the record ? I don’t see any option to use ACLs to then determine which CUD operations are allowed once you HAVE retrieved the record on screen.


Rajith
Sidekick (Partner)
Forum|alt.badge.img+6
  • Author
  • Sidekick (Partner)
  • Nov 12, 2026 4:58 PM UTC

it says something about


“Apply to CRUD : Each Projection Entity is structured to permit specific CRUD operations. Upon choosing the projection entity, you can determine which CRUD operation to implement with the ACL. If the user applies 'Read' it automatically will be applied to CUD operations, and if the 'Read' is not selected the user is able to apply any desired combination of CUD operations. Operations that are not permitted at the design phase will be designated as Not Applicable (NA)”


here, not sure what it means.

https://docs.ifs.com/techdocs/26r2/030_administration/010_security/008_custom_data_access_control/020_apply_acl_to_projection/


Abdul
Superhero (Partner)
Forum|alt.badge.img+20
  • Superhero (Partner)
  • Nov 12, 2026 5:45 PM UTC

Hi ​@Rajith and ​@SimonTestard,

It is possible to configure CRUD actions for user/user group through ACL.

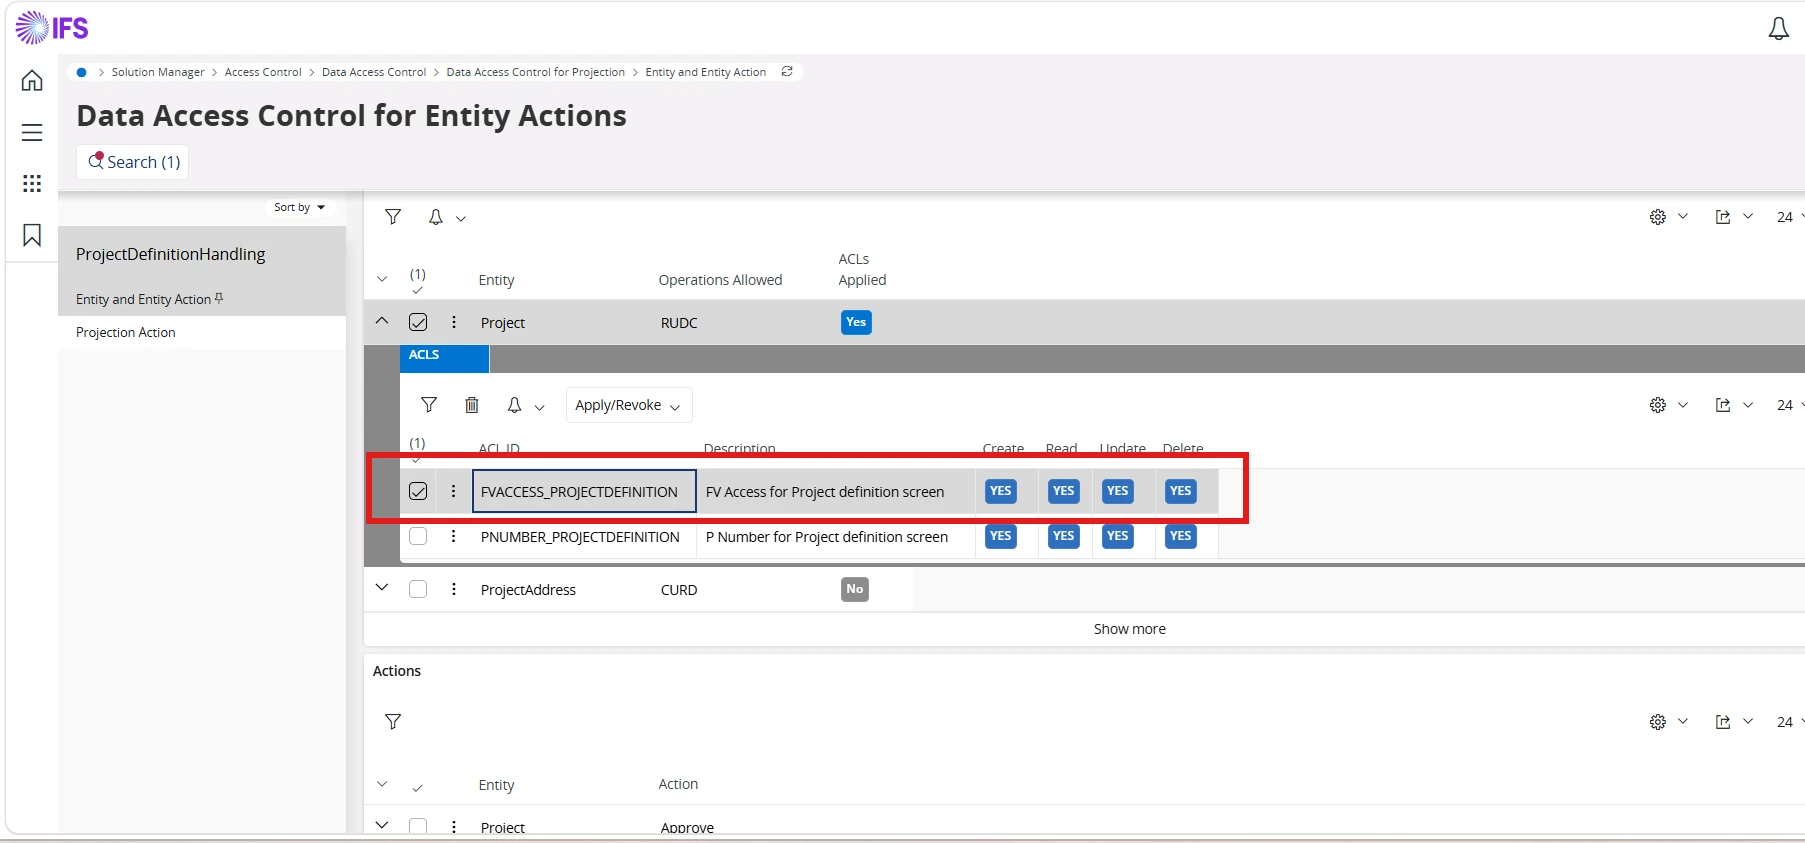
In my current implementation, we configured ACL for Project Definition screen where customer creates two types of Projects viz. Project Template (which will only be used as a source Project for creating new Projects) and Transactional Projects. 

Only specific user groups (IT Admin) are allowed to alter Project Template information while other user group are not allowed.

We used Projection based ACL since there were some challenges with entity based ACL.


Forum|alt.badge.img+12
  • Hero (Customer)
  • Nov 12, 2026 8:02 PM UTC

Oh cool I didn’t realize you could set the ACL on specific entity actions, that’s good to know, thanks both !


Rajith
Sidekick (Partner)
Forum|alt.badge.img+6
  • Author
  • Sidekick (Partner)
  • Nov 17, 2026 4:24 AM UTC

Cheers ​@Abdul , could you share your filters and the setup please?


my requirement


when we grant CustomerOrderHandling, users in user group A wants to Create Customer Orders and users in user group B wants update Customer Orders but not create.


best regards


Abdul
Superhero (Partner)
Forum|alt.badge.img+20
  • Superhero (Partner)
  • Nov 18, 2026 4:00 AM UTC

Hi ​@Rajith.

Sorry for late reply!

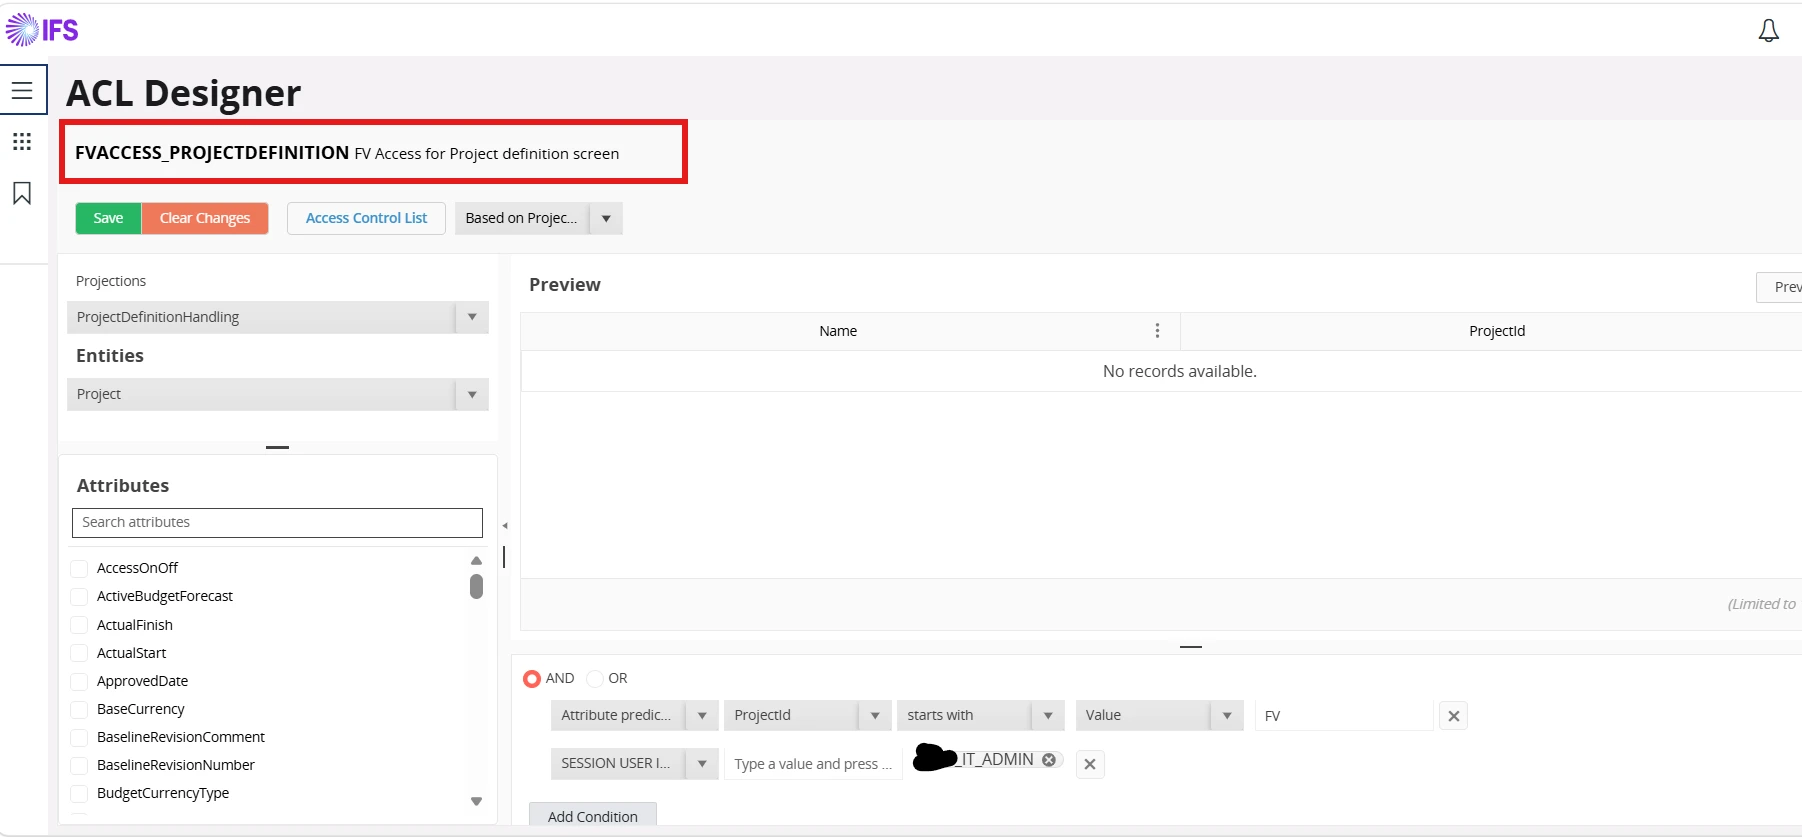
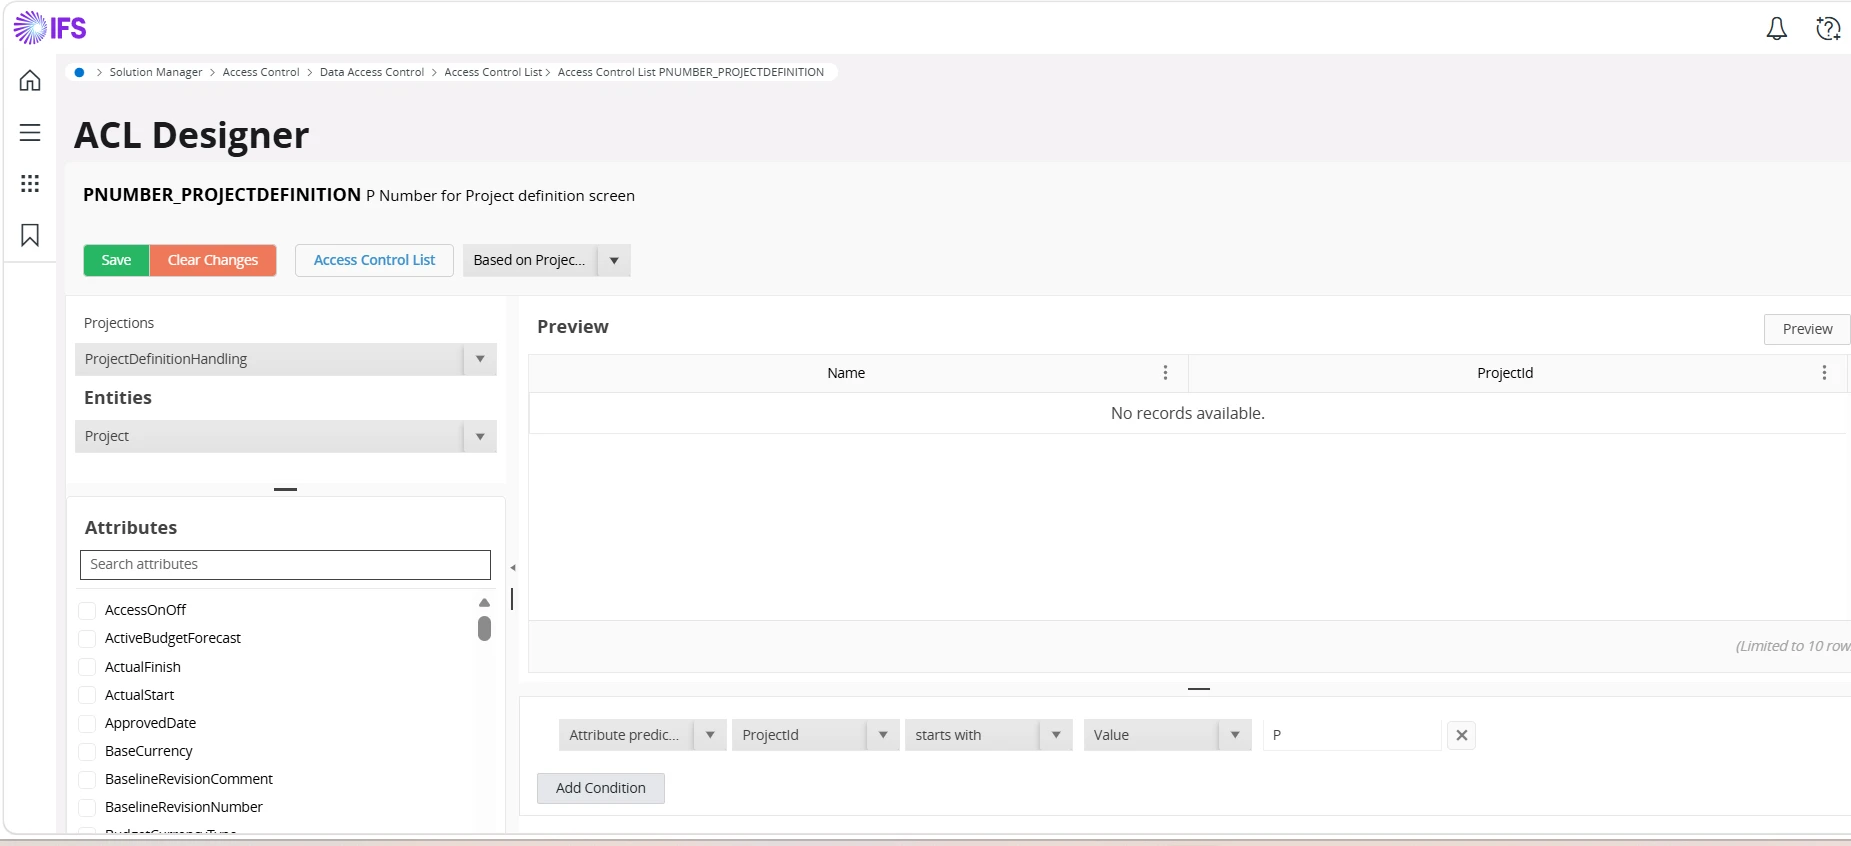
Please find screenshots below.

We have created following two ACLs.

1. FVACCESS_PROJECTDEFINITON - Will provide Project Template access to IT Admin User Group which will full access for project template.

   2.  Applied DAC for Project entity for  FVACCESS_PROJECTDEFINITON


3. Likewise configured another ACL to access Transactional Project where no User Group condition was added means all users can access Transactional Projects.

  4. Repeat step number 2 ​to apply DAC again for Project entity.

Hope this will help.​​​​​​

  1.  

dsj
Ultimate Hero (Partner)
Forum|alt.badge.img+22
  • Ultimate Hero (Partner)
  • Nov 18, 2026 8:47 AM UTC

​@Rajith 

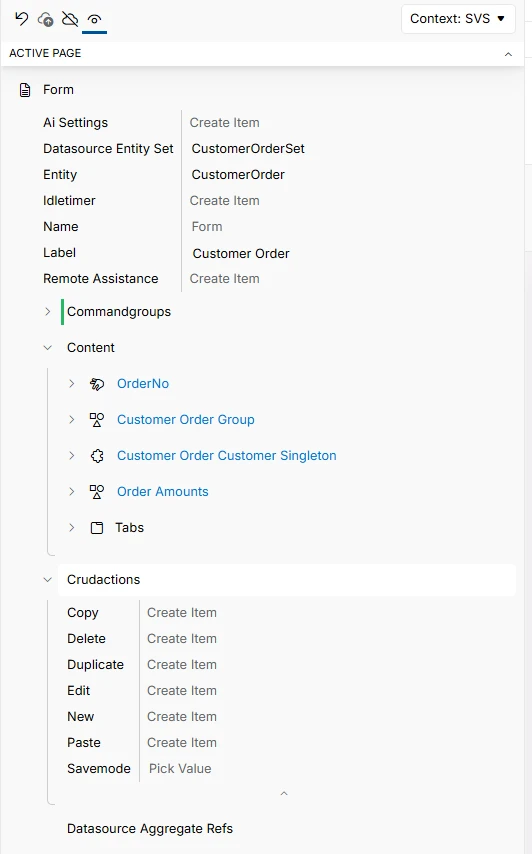
You could control CRUD in a page using the page designer context.

If you do it this way, the CRUD actions needs to apply in header and tabs seperaely.

Not the ideal way but it works :)


Rajith
Sidekick (Partner)
Forum|alt.badge.img+6
  • Author
  • Sidekick (Partner)
  • Nov 19, 2026 3:18 PM UTC

Many thanks ​@Abdul, I will give that a try.


Also thanks ​@dsj that seems a good one, but we only maintain a single context, wonder if we can add conditions to each CUD action as we do for other entries. must try this.


best regards